AI Governance in Banking: Model Risk, Controls, and Oversight
Banks should map AI use cases to existing model-risk, security and operational-risk responsibilities.
Banks should map AI use cases to existing model-risk, security and operational-risk responsibilities.
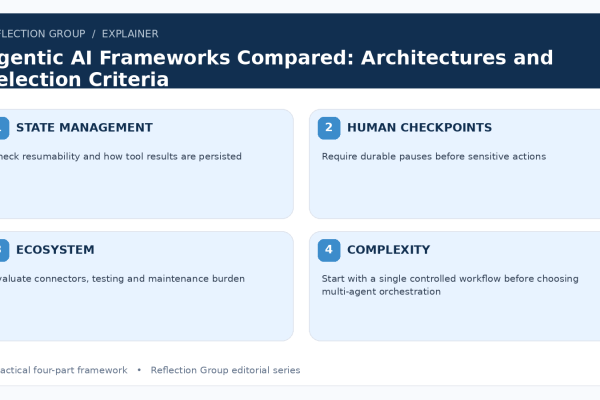
Pick a framework based on control flow and failure handling, not how many agents a demo can spawn.
The right evaluation stack depends on whether a team needs experiments, production traces or human review.
A single LLM score hides trade-offs; choose separate metrics for task quality, grounding and operational reliability.
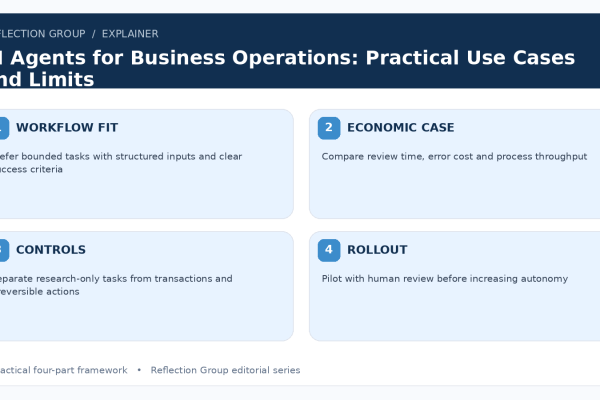
The best agent use cases are repetitive, observable and reversible, with clear ownership of exceptions.
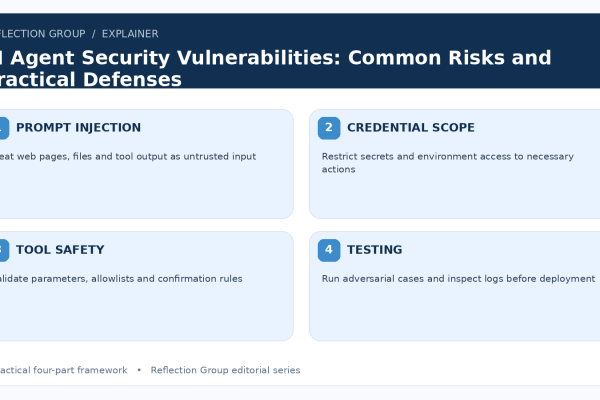
Agent security must consider instructions hidden in retrieved documents and unintended privilege escalation.
Agents differ from chat assistants because they can invoke tools and change systems; that requires action-level boundaries.
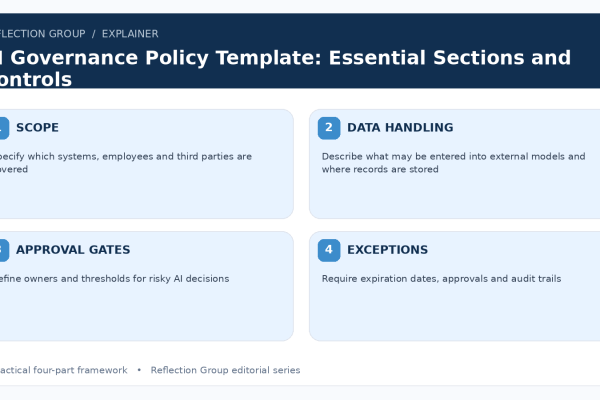
A usable policy names decision makers, permitted data, review procedures and measurable exceptions.
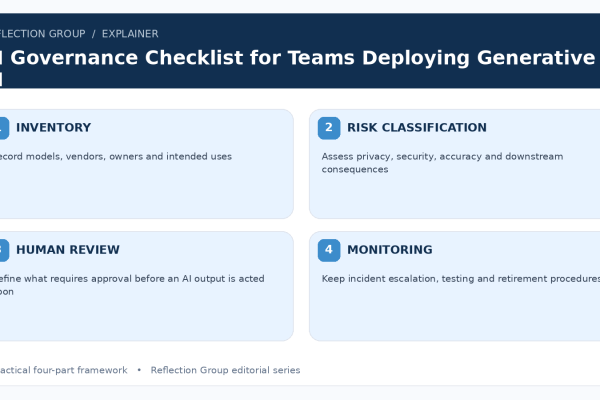
AI governance should result in owned controls, not merely a policy PDF nobody uses.
Healthcare discovery cannot be optimized responsibly by manufacturing certainty; source integrity and clinical review are non-negotiable.